We teach AWS for the real world - not for certifications. Join more than 10,500 developers learning how to build real-world applications on AWS.
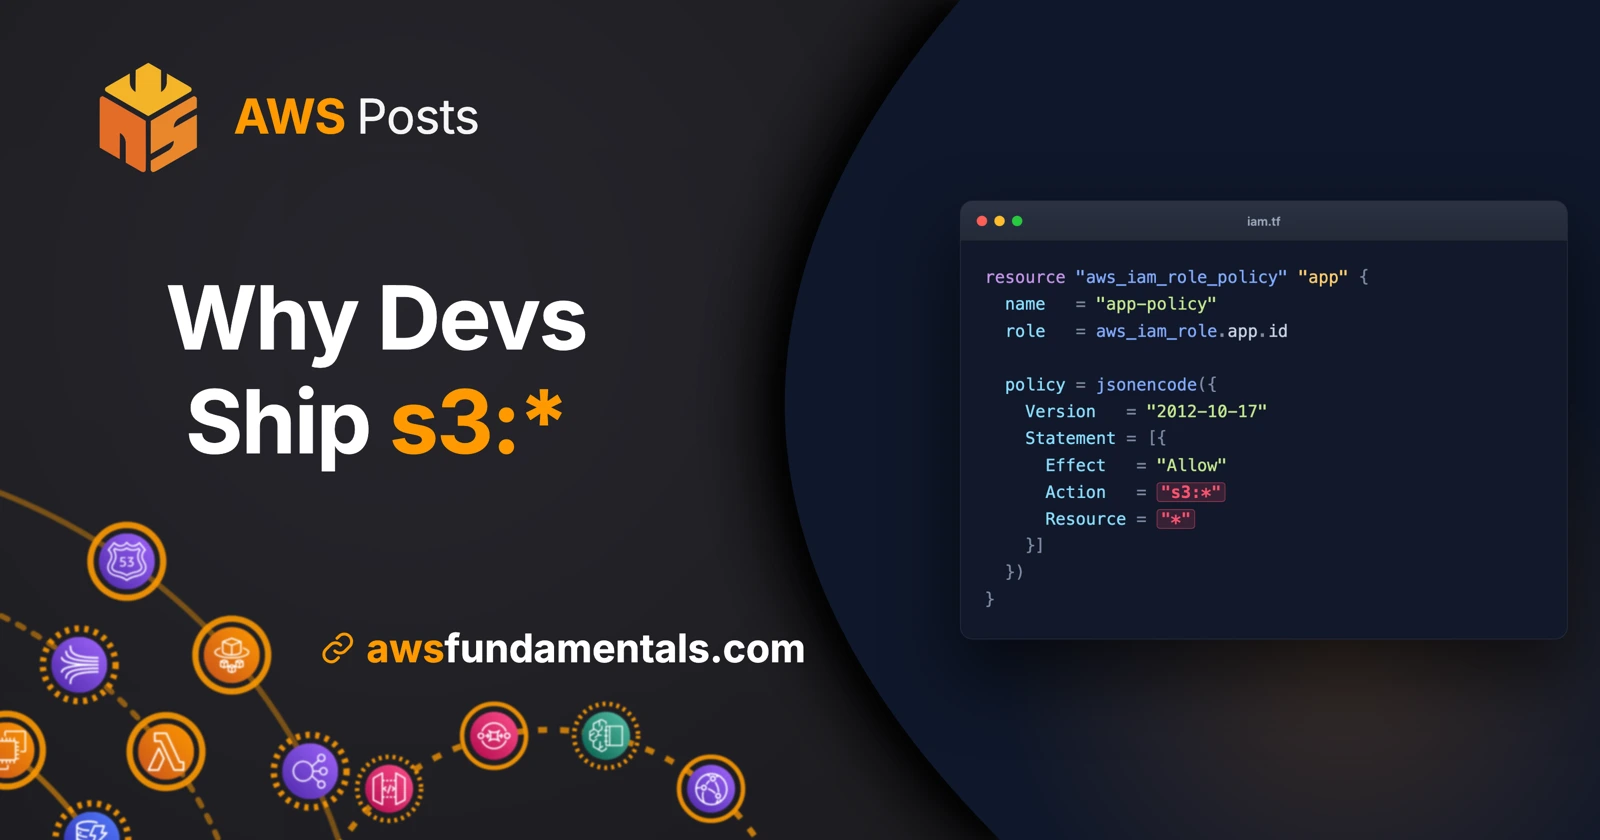
Why devs ship s3:* (and the fix)
|
AWS FOR THE REAL WORLD
⏱️
Reading time: 10 minutes
🎯
Main Learning: Wildcards come from the tooling, not from laziness. Put least privilege at the account level
and let an agent write the policies.
Hey Reader 👋🏽 I have shipped my share of s3:* at unusual hours and told myself I would refactor it later - which obviously never happened 😅 So when someone on r/aws asked why developers can't write least privilege policies and put it down to laziness, I was excited to read through all of the comments. They just explain what it actually costs to avoid them: one denied action at a time, ten minutes per deploy, and a deadline that doesn't move - very relatable, especially if you use CloudFormation in any way 😬 In this issue: the five reasons the thread brought up, where the OP still has a point, and the setup I use instead 🫡 Sponsored by Typesense, a tool we run ourselves.
That's it for this issue. If you take one thing away: stop paying the least privilege cost per role. Put the hard boundary at the account level with separate accounts and SCPs, and let your IaC and your agent write the scoped grants. And read what comes out. A policy nobody reviewed is not least privilege, no matter who typed it 😅 See you in the next one! Sandro & Tobi |
AWS for the Real World
We teach AWS for the real world - not for certifications. Join more than 10,500 developers learning how to build real-world applications on AWS.
⏱️ Reading time: 15 minutes 🎯 Main Learning: A public container on AWS for $7 a month, with no VPC to own. 📝 Blog Post 🤝 Sponsored by AWS. What we built, what it cost and what we think of it are our own. Hey Reader 👋🏽 Your first container on ECS comes with homework: a VPC, subnets in two Availability Zones, a load balancer, security groups, a certificate and a task role. Express Mode creates most of it for you now (App Runner's successor, so ECS abstraction number three), but it all lands in...
AWS FOR THE REAL WORLD ⏱️ Reading time: 6 minutes 🎯 Main Learning: You cannot skip a level of AWS observability. Structured logs come first, then the AI agent that reads them for you. 📝 Blog Post 📂 Claude Code agent (free gist) 🎬 Watch on YouTube Hey Reader 👋🏽 This week I'm bringing back one of our most-read posts: the 3 levels of AWS observability. A lot of you joined after it went out in May, and the topic fits this week perfectly. Because the real question isn't "do I have logs?" anymore....
⏱️ Reading time: 11 minutes 🎯 Main Learning: Measure NAT traffic first. CI runners rarely need NAT at all. 📝 Blog Post Hey Reader 👋🏽 NAT Gateways are one of those things you set up once and never look at again (probably!) 😅 Until NatGateway-Bytes shows up near the top of the bill, filed under EC2-Other - thanks AWS! I think they've made this on purpose to hide these significant networking related costs somewhere and made it hard to reflect on! The hourly fee is predictable, sure. But the...