We teach AWS for the real world - not for certifications. Join more than 10,500 developers learning how to build real-world applications on AWS.
My fullstack AWS stack in 2026
|
AWS FOR THE REAL WORLD
⏱️
Reading time: 6 minutes
🎯
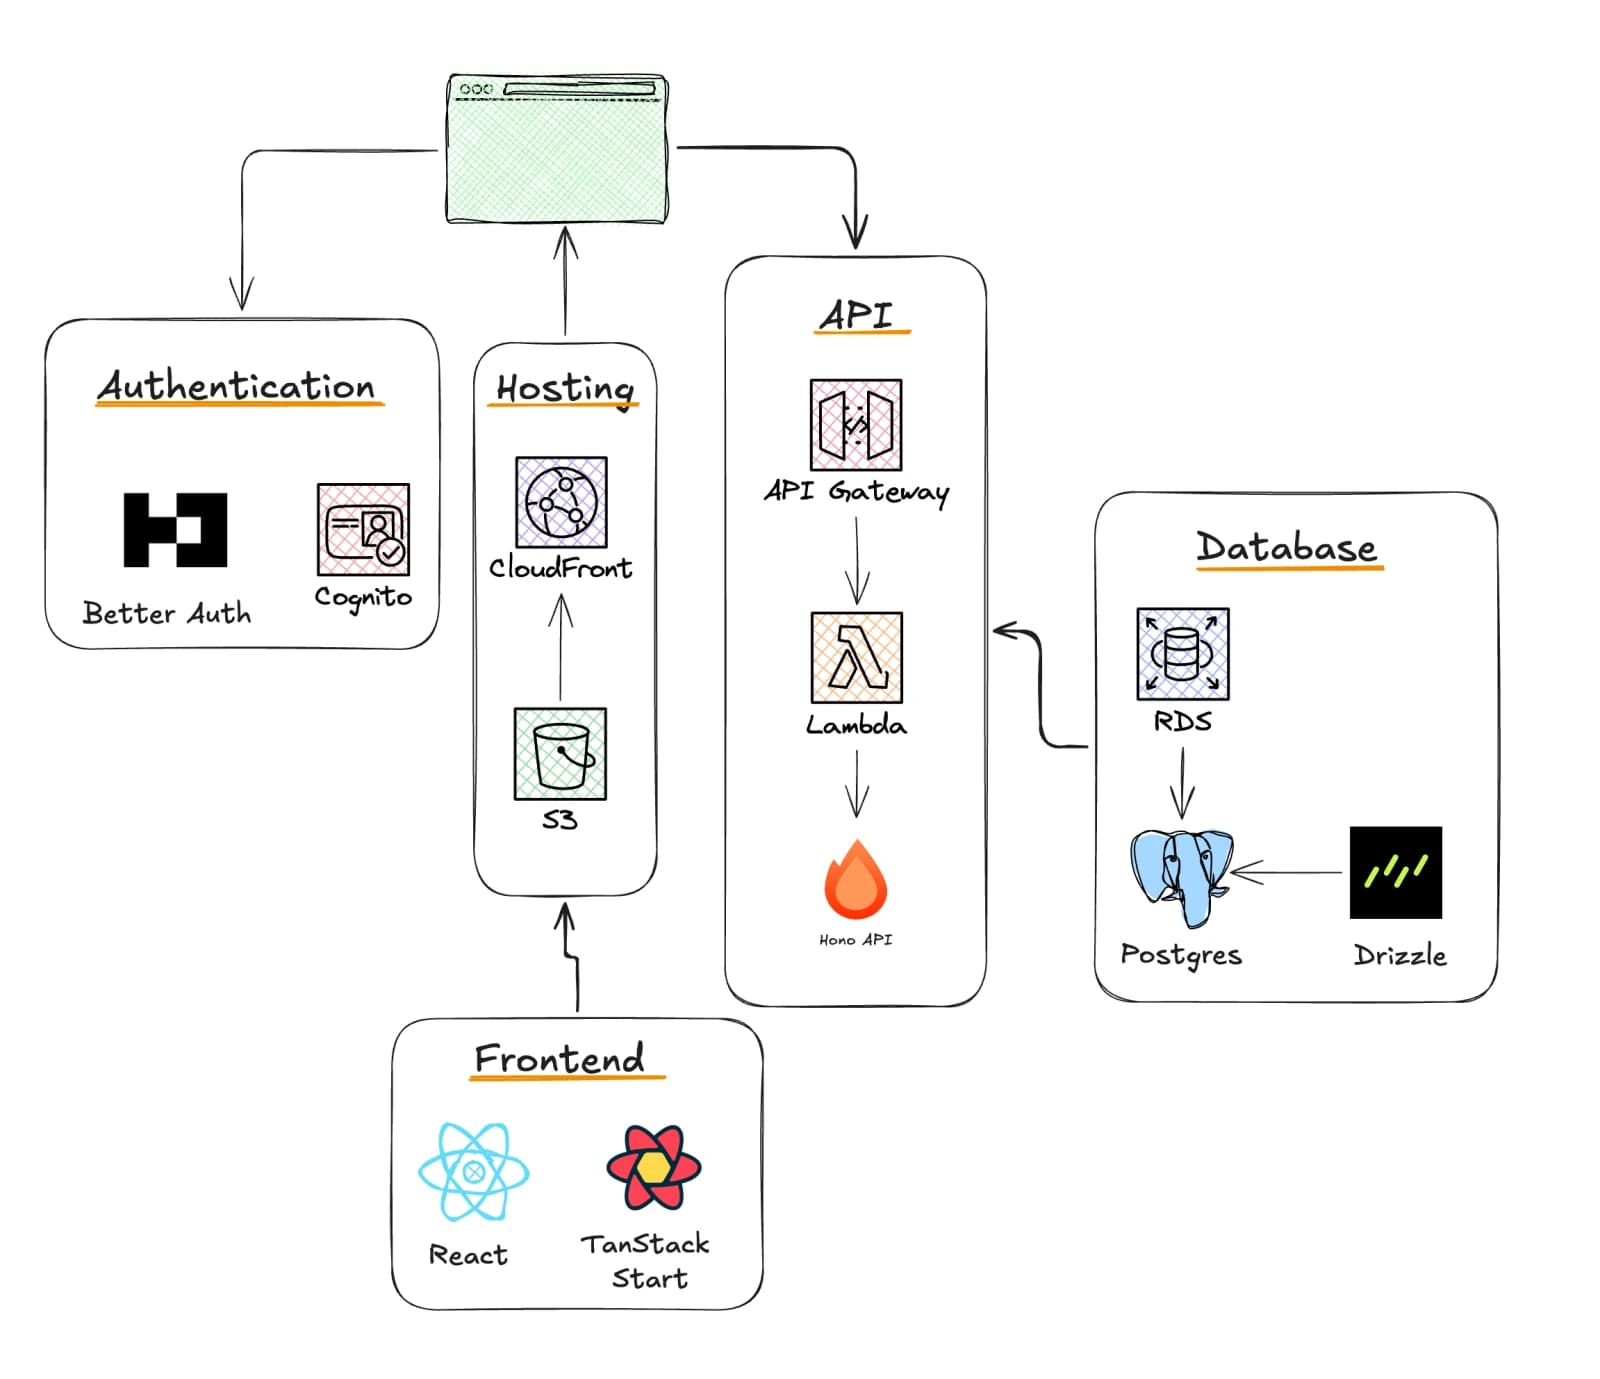
Main Learning: One stack, reused for every project. Hono on Lambda, Postgres with Drizzle, a TanStack SPA on
S3 and CloudFront, and Better Auth for login.
Hey Reader 👋🏽
Over the past few years we switched up tech stacks a lot. That taught us what actually matters in a stack and what is just noise.
We stopped switching the tech stack. Every project gets almost the same tech stack now. And this is the one.
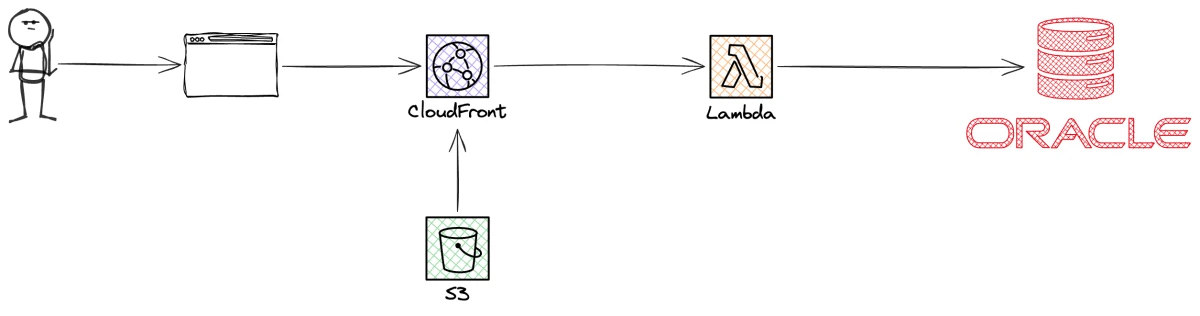
Sponsored by Oracle. I built and ran the demo myself.
How does your stack look? |

AWS for the Real World
We teach AWS for the real world - not for certifications. Join more than 10,500 developers learning how to build real-world applications on AWS.
⏱️ Reading time: 21 minutes 🎯 Main Learning: Same CloudFront logs: 12.5s through Kinesis, S3, Glue and Athena, about 1s through Tinybird's managed ClickHouse. 📝 Blog Post Hey Reader 👋🏽 We've been running Plausible for the analytics on awsfundamentals.com. Good software, no complaints. We still wanted the data to be ours: our retention, our schema, nobody's script in the visitor's browser. So we built the dashboard ourselves. Twice, on two different backends, fed by the same CloudFront logs....
AWS FOR THE REAL WORLD ⏱️ Reading time: 11 minutes 🎯 Main Learning: A Karpenter NodePool is a placement policy, not an instance preference. Pin one instance family, and a Spot shortage moves your fleet across availability zones, where every internal call starts costing $0.01 per GB. 📝 Blog Post Hey Reader 👋🏽 Important off topic things first: Sandro got married! 🎉We were in Munich for it and it was a fantastic day! ☀️Highly recommend a wedding over sprint planning or fighting with AWS...
AWS FOR THE REAL WORLD ⏱️ Reading time: 10 minutes 🎯 Main Learning: Wildcards come from the tooling, not from laziness. Put least privilege at the account level and let an agent write the policies. 📝 Blog Post Hey Reader 👋🏽 I have shipped my share of s3:* at unusual hours and told myself I would refactor it later - which obviously never happened 😅 So when someone on r/aws asked why developers can't write least privilege policies and put it down to laziness, I was excited to read through all...