SCPs, RCPs, and a kill switch: a real AWS org setup


AWS FOR THE REAL WORLD
⏱️
Reading time: 12 minutes
🎯
Main Learning: Wrapping a multi-account AWS org in multiple layers of guardrails, featuring SCPs, RCPs, CloudTrail and Bugdet Actions
📝

Hey Reader 👋🏽
As you hopefully know, we're really obsessed with security, observability and auditability.

That's why we've carefully crafted our AWS Organization's setup. 🏗️

In this issue, we want to walk you through our most important guardrails!

Including all the whats and whys. 😊

Sponsored
Archera

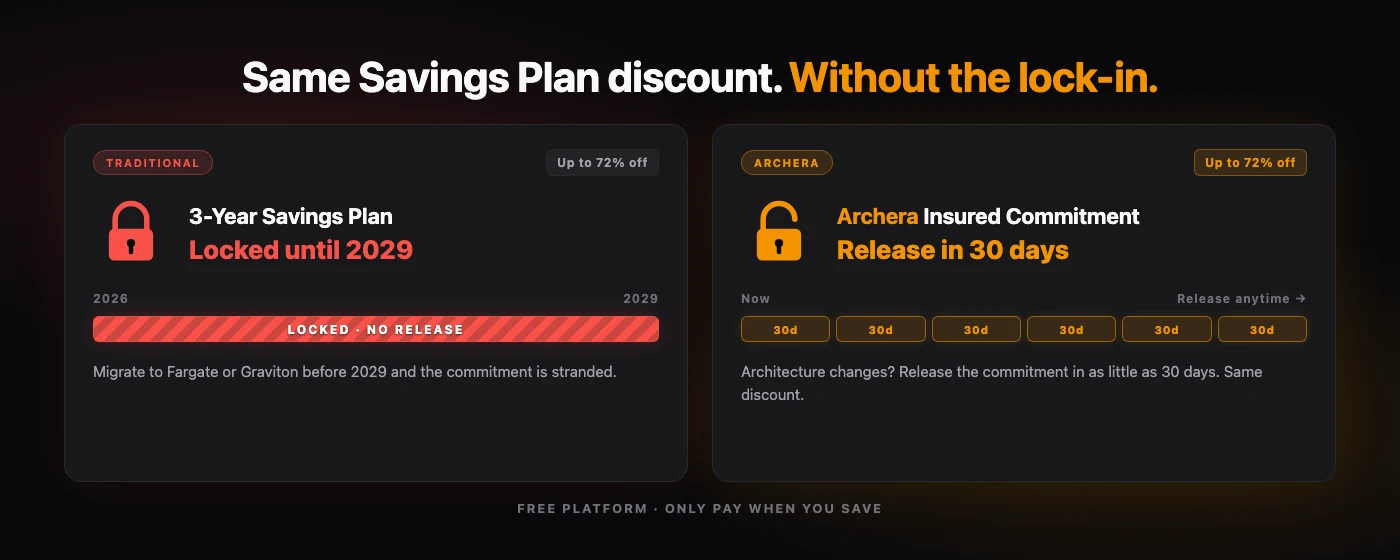
AWS Savings Plan pricing, without the lock-in

Same Savings Plan discount — Archera insured commitments release in 30 days vs traditional 3-year lock-in

A 3-year Savings Plan locks you in. Migrate to Fargate or Graviton before it expires, and the commitment is stranded. Archera's insured commitments give you the same discount with a release guarantee — release in as little as 30 days when your architecture changes. Free platform; you only pay when you save.

Sponsored by Archera

📚 This Week's Deep Dive

A single AWS account is fine until it isn't 😅 The moment you have more than one workload, the math mostly flips! You want separation, isolation, per-project billing, and the same set of guardrails everywhere!

We rebuilt our AWS Organization from the ground up in Terraform. Three OUs, six member accounts, no IAM users anywhere, Identity Center for humans and GitHub OIDC for CI. The post walks through the four layers that turn a bare org into something we trust ourselves with:

  • SCPs - block expensive instance families, pin everyone to four regions, deny Bedrock org-wide, kill CloudTrail tampering, and enforce MFA on every IAM user.
  • RCPs - enforce TLS on S3, SQS, and Secrets Manager, and slam shut S3 public access — even for callers outside the org.
  • CloudTrail → EventBridge → Lambda - an org-wide trail and a small Node.js Lambda that fans events out to SES and Slack, color-coded by severity.
  • The kill switch - a $50 monthly budget on the Sandbox OU paired with a Budget Action that automatically attaches a deny SCP at 80% actual spend.

The post is honest about the sharp edges too: SCPs do not restrict the root user of the management account and AWS Budgets data lags 8 to 12 hours so no native AWS feature truly enforces a real-time spending cap.

📰 This Week in AWS

🤖Claude Platform on AWS is now GA

Anthropic's native Claude Platform is now available straight through your AWS account — same APIs, Managed Agents, Skills, and MCP connectors as Anthropic offers directly. Different from Bedrock: Anthropic operates the inference stack, AWS handles the billing relationship. Read More →

🛡️AWS Organizations doubles the SCP quotas

You can now attach up to 10 SCPs per node (root, OU, or account) instead of 5, and a single SCP can be up to 10,240 characters instead of 5,120. Available everywhere automatically. If you have ever fought the old limits while consolidating policies, this is a real quality-of-life bump. Read More →

🧰Agent Toolkit for AWS launches

Official AWS MCP servers, plugins, and 40+ agent skills for CloudFormation, serverless, data pipelines, and more. Works with Claude Code, Cursor, and Kiro out of the box. No extra cost — you pay only for the AWS resources the agents actually use. Read More →

If you take one thing away: the value of a multi-account setup is what you build around the accounts, not the accounts themselves.

A "bare" AWS Organization with no SCPs, no audit trail, and no spending guardrails is just multiple places (=accounts) for the same mistake(s) to happen.
See you soon!
Sandro & Tobi

AWS for the Real World

We teach AWS for the real world - not for certifications. Join more than 10,500 developers learning how to build real-world applications on AWS.

Read more from AWS for the Real World

AWS FOR THE REAL WORLD ⏱️ Reading time: 11 minutes 🎯 Main Learning: A Karpenter NodePool is a placement policy, not an instance preference. Pin one instance family, and a Spot shortage moves your fleet across availability zones, where every internal call starts costing $0.01 per GB. 📝 Blog Post Hey Reader 👋🏽 Important off topic things first: Sandro got married! 🎉We were in Munich for it and it was a fantastic day! ☀️Highly recommend a wedding over sprint planning or fighting with AWS...

AWS FOR THE REAL WORLD ⏱️ Reading time: 6 minutes 🎯 Main Learning: One stack, reused for every project. Hono on Lambda, Postgres with Drizzle, a TanStack SPA on S3 and CloudFront, and Better Auth for login. 📝 Blog Post Hey Reader 👋🏽we've build a lot of fullstack applications so far: client projects side projects (this one, shopify apps, etc.) example tutorial apps Over the past few years we switched up tech stacks a lot. That taught us what actually matters in a stack and what is just...

AWS FOR THE REAL WORLD ⏱️ Reading time: 10 minutes 🎯 Main Learning: Wildcards come from the tooling, not from laziness. Put least privilege at the account level and let an agent write the policies. 📝 Blog Post Hey Reader 👋🏽 I have shipped my share of s3:* at unusual hours and told myself I would refactor it later - which obviously never happened 😅 So when someone on r/aws asked why developers can't write least privilege policies and put it down to laziness, I was excited to read through all...